
Managed SOC monitoring & triage
Review security alerts from supported existing platforms, validate suspicious activity, prioritize risk, and escalate actionable findings within the agreed monitoring schedule.
Phantom Cybersecurity provides managed SOC services, including security monitoring, alert triage, and threat investigations. Our analyst works with your existing security tools to identify threats and deliver clear, actionable guidance.
We connect the signals from your existing tools, investigate meaningful alerts, and help your team take the right next step.
Analyst-led security operations aligned with your environment.
Monitoring hours, supported integrations and response authority are agreed during scoping.
From day-to-day security monitoring to deeper investigations and improved detections, Phantom helps take the operational burden off your team. Coverage hours, integrations and response authority are agreed during scoping.
Review security alerts from supported existing platforms, validate suspicious activity, prioritize risk, and escalate actionable findings within the agreed monitoring schedule.
Investigate suspicious behavior, connect evidence across sources, identify affected systems, and guide containment, escalation, and next steps.
Improve detection rules, tune noisy alerts, identify coverage gaps, and make better use of the capabilities already in your environment.
Identify gaps in logging, identity protections, endpoint coverage, and security operations workflows.
Get readable investigation summaries, prioritized findings, and recommended next steps grounded in available telemetry.
Build escalation paths, improve playbooks, and establish practical procedures before an incident occurs.
We build around your existing SIEM, EDR/XDR, identity, email, firewall, and cloud security investments where supported. No mandatory platform replacement; any gaps or optional additions are discussed up front.
Make informed security decisions with focused consulting backed by hands-on experience protecting private enterprise and government networks. Phantom helps organizations assess risk, strengthen existing controls, and build an achievable security improvement plan—without pushing unnecessary products.
Review security controls, exposed attack surfaces, logging visibility, and operational gaps. Receive prioritized recommendations grounded in your environment.
Evaluate MFA, Conditional Access, privileged access, account protections, and Microsoft 365 security configurations to reduce identity-based risk.
Assess firewall controls, endpoint protection, segmentation, detection coverage, and how your existing tools work together. Identify improvements without unnecessary replacement.
Develop escalation procedures, review response playbooks, establish roles, and improve your team's ability to respond effectively when security incidents occur.
Tell us about your environment and goals. We'll discuss a consulting scope that fits your organization.
We focus on what happened, what the evidence supports, and what your team should do next.
Map key assets, existing platforms, available telemetry, business risk, and escalation requirements.
Work from your identity, endpoint, email, firewall, and SIEM data wherever supported by your environment.
Validate suspicious behavior, preserve context, and distinguish confirmed findings from leads.
Deliver concise reporting and response guidance aligned to your agreed service scope.
Many organizations already have valuable security capabilities they are not using to their full potential. Phantom is designed to complement your tools, workflows, and licenses—not force a replacement.
Specific platforms, access methods, response authority, and monitoring hours are confirmed during scoping. No affiliation with third-party vendors is implied.
Alongside our managed security services, we are developing a separate investigation application designed to organize evidence, connect events and help analysts reach defensible conclusions.
The interface shown is Concept B: Evidence Ledger, a proposed UI design—not a live SOC monitoring dashboard, a released application or a service guarantee.
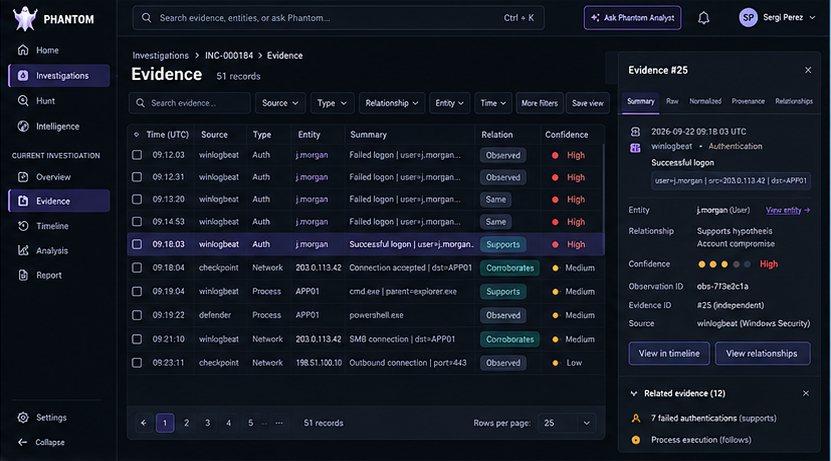 CONCEPT B · PROPOSED APPLICATION UI · NOT RELEASED
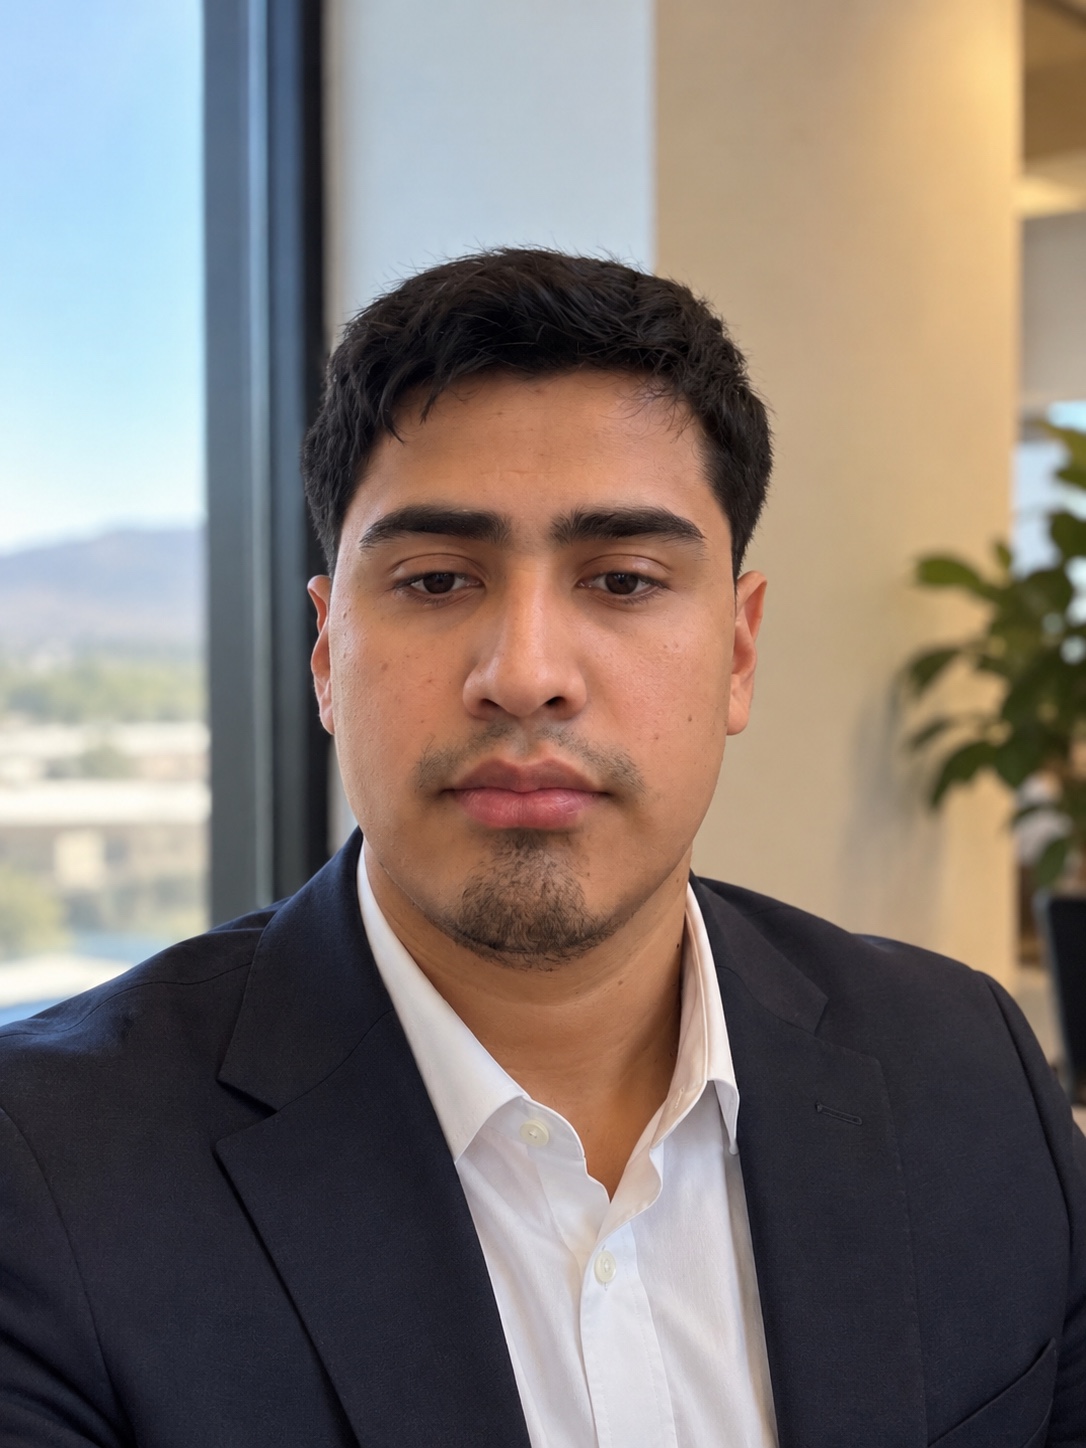
Phantom Cybersecurity has been a dream of mine for some time. My experience helping protect private enterprise networks and government networks has shaped my approach to cybersecurity—from security monitoring and incident investigation to safeguarding identities, endpoints, and critical infrastructure. I founded Phantom to bring that same vigilance, hands-on expertise, and personal commitment to organizations seeking dependable cybersecurity support. Based in Santa Barbara, California, our mission is to help businesses protect what matters most.
“I can do all things through Christ which strengtheneth me.”Philippians 4:13 · KJV
Tell us what you need monitored, what tools you currently have, and where your team needs help. We'll define a practical service scope, coverage window, and escalation process.
Whether you need ongoing alert triage, threat investigation, stronger detections, or incident response guidance, we can put your existing tools and telemetry to better use.
Please do not submit passwords, log extracts, personal records, incident details, or other sensitive information here.